Is It Time to Start Outsourcing Cyber Security for Your Business?

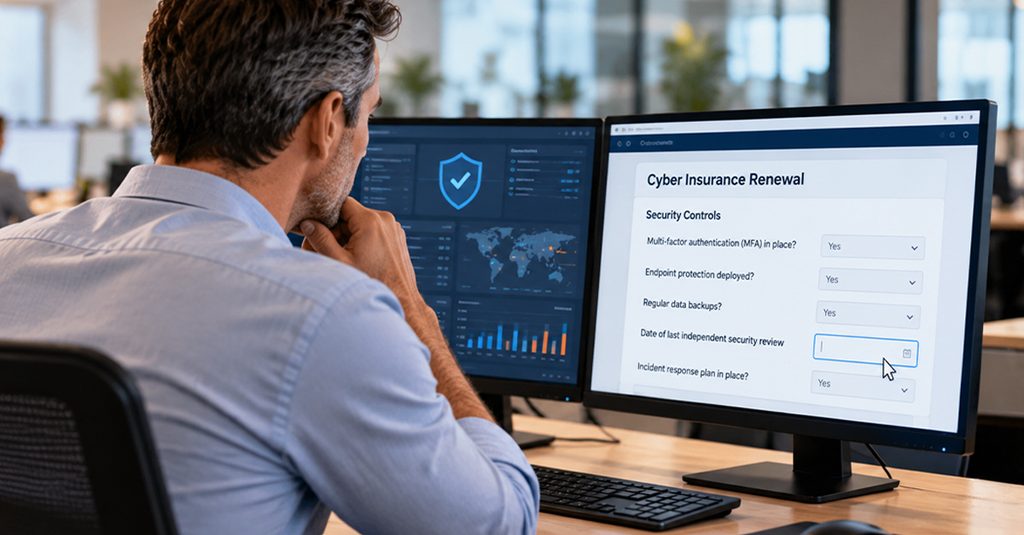
Your cyber insurance renewal is open on your second screen. You tick yes for multi-factor authentication, because your IT provider switched it on last year. The next field asks for the date of your last independent security review. The box sits empty. 

That empty field isn’t your IT provider dropping the ball. An independent review was never in their agreement, so the job sat with you. 

In my experience, outsourcing cyber security means adding specialist skills while your current IT support stays put. Whether you need that depends on your risks and your current team’s capacity. 

Until this form asked, there was no reason for it to come up. 

Quick Summary

Outsourcing cyber security means bringing in a specialist to sit beside the IT provider you already have. It makes sense once your business has outgrown its security setup, or when an insurer or client asks for proof you can’t put your hands on. A gap analysis ranks what to fix first.

WHAT ARE SPECIALIST CYBER SECURITY SERVICES AND WHAT WOULD I GET? 

Specialist cyber security services are the people you bring in to find where your business is exposed and help you close it, once or on an ongoing basis. 

Your IT support keeps your systems running. A specialist looks at them the way an attacker would, starting with the old laptop that missed its last few updates. 

The first piece of work is a cyber security maturity assessment, which shows where you sit against a recognised framework. The gap analysis after it tells you what to fix first. Governance is the paperwork your insurer keeps asking about, from security policies to an incident response plan your team can pick up on a bad Monday. Compliance alignment checks all of it against the Privacy Act, or that clause buried in a client contract. 

Then there’s the hands-on work. Managed security services put a team on your alerts at 3am so you’re not the one watching. Penetration testing is a controlled attack you pay for, so the weak spots turn up on paper first. 

DO I NEED A CYBER SECURITY SPECIALIST IF I ALREADY HAVE AN IT PROVIDER? 

You might not need a separate specialist if your IT provider already covers the testing and reporting your risks call for. 

Some managed IT providers run their own security teams. The gap shows when your provider’s working hours all go to helpdesk tickets, or a client wants testing that your agreement leaves out. 

Specialist support isn’t automatically independent. If your IT provider also assesses your security, ask how they keep those roles apart. If you’d like a governance-led view, ADITS’ partner Advanta Advisory offers cyber security consulting. 

WHY AREN’T MY SECURITY TOOLS ENOUGH ON THEIR OWN? 

Security tools only protect you once they’re set up for your business and watched by a person who acts on alerts. 

That multi-factor authentication tick is real. On Microsoft 365 Business Premium, you’re also paying for Microsoft Defender for Business, which watches your devices for threats, and Microsoft Entra ID P1, Microsoft’s identity and access management tool. Both need configuring for your business before they earn their keep. 

The question is who configures them. If your IT agreement includes security configuration reviews, it’s your provider. If it doesn’t, it’s the specialist you bring in, and until then it’s you. 

Once you can see what each service does, you can match it to the gap on your form. When that gap is worth closing comes next. 

Desk view of two monitors, the second showing a cyber insurance form with the cursor hovering over an empty Date of last independent security review field.

WHEN WOULD SPECIALIST CYBER SECURITY SERVICES ADD THE MOST VALUE FOR ME? 

Specialist cyber security services pay off most when your security is still set up for the business you were three years ago. 

A second site adds a network your IT provider secures from a distance. Switch on Microsoft Copilot, the AI assistant in Microsoft 365, and it’ll happily find the payroll spreadsheet for a staff member who had access to that folder all along and never knew it. 

Every change like that deserves a second look from a specialist, and these next three things show where that look matters most. 

HOW CAN SPECIALIST SUPPORT HELP ME MEET COMPLIANCE REQUIREMENTS? 

Specialist support helps you meet compliance requirements by giving you something to hand over when an auditor or insurer asks, like documented controls and a dated review. 

The Privacy Act is law. Under Australian Privacy Principle 11, a covered business must take reasonable steps to protect personal information, including technical and organisational measures. Businesses turning over $3 million or less are generally exempt, for now. 

Insurance conditions and client questionnaires are contractual obligations. A specialist assesses your controls against whichever applies and prepares the evidence with you. That doesn’t guarantee compliance, and a provider who promises it is overselling. 

HOW DO I KNOW HOW MATURE MY CYBER SECURITY IS AND WHERE THE GAPS ARE? 

A cyber security maturity assessment measures you against a recognised framework, and a cyber security gap analysis ranks what’s missing by risk. 

The assessment scores you against a framework such as SMB1001, a standard for small and medium businesses, or the Essential Eight, the Australian Signals Directorate’s baseline strategies. Your maturity is the level you reach, and the gaps are the controls between you and the next one. 

My test for a good gap analysis is whether you could explain the top three findings to your business partner. Without an IT person in the room. 

WHAT DOES A MORE STRATEGIC APPROACH TO SECURITY LOOK LIKE? 

A more strategic approach to security puts your fixes on a prioritised list with its own budget line and a standing spot in your leadership meetings. 

The people approving that budget line usually weren’t in the room for the gap analysis. Cyber security training for executives gives them enough grounding to weigh a risk, and to know who picks up the phone when an incident hits. It changes the questions they ask at the next board meeting. 

AHEAD OF THE AUDITORS 

When the 2014 Privacy Act amendments took effect, Centacare North Queensland wanted to understand its new obligations. ADITS helped Centacare plan for a possible data breach and strengthen its security governance. Centacare’s audits found it compliant with the requirements, and its cyber security processes passed every test. 

Read the case study

None of this replaces your IT provider. It hands them a list of priorities to work from. 

HOW DOES OUTSOURCING CYBER SECURITY WORK ALONGSIDE MY EXISTING IT? 

Outsourcing cyber security sits alongside your IT. Your provider still answers the helpdesk calls and patches the laptops. The specialist comes in to test what’s been set up and tells you, in writing, what needs fixing. 

Where I’ve seen this go wrong is the bit in between. The report goes to you, you forward it to your IT provider, and by the next renewal half of it is still open. Before the report lands, agree who’s chasing each fix and put a name next to it. 

WHO WOULD BE RESPONSIBLE FOR WHAT IN MY BUSINESS? 

In a shared security setup, the calls on risk and spend stay with you. Your IT provider does the hands-on work, while the specialist checks it and keeps watch. 

Who What they own 
You and your leadership team Signing off what gets fixed and what it costs 
Your IT provider Running your systems and making the fixes on the list 
Your specialist provider Assessment, advice, testing or monitoring 
Shared Tracking fixes to completion and coordinating during an incident 

Your agreements decide the final split. If a task isn’t written into either one, treat it as yours until it is.

WHAT ARE MY OPTIONS FOR BRINGING IN SPECIALIST SUPPORT? 

Specialist support doesn’t have to mean a long contract. It can be one job before your renewal, or it can stay on. 

A one-off assessment is the quick version. You get the dated review your insurer wants, plus a list of gaps. Fixing those is a separate project, done once, and then your IT provider takes it from there. If client questionnaires keep landing on your desk, ongoing advisory means you’ve got a specialist to ring about them. Co-managed security works with your internal IT person, and fully managed security operations watch your systems day and night. 

My advice is to start with the smallest model that fills your gap. Who delivers it matters just as much. 

WHAT SHOULD I LOOK FOR IN A CYBER SECURITY PROVIDER? 

A good cyber security provider can tell you which framework fits a business your size, and what you’ll hold at the end. 

I judge providers on whether they respect the IT relationship you already have, and whether their reports make sense to the person paying. Take these questions into your first meeting. 

FOUR QUESTIONS TO ASK 

  1. Which framework suits a business our size, and why? 
  2. How will you work with our IT provider? 
  3. Do we get a report, a roadmap or ongoing reporting? 
  4. How will you explain our risks to leadership without jargon?

The answers show whether a provider can put a date in that box you’d stand behind.  

WHAT WOULD SPECIALIST SUPPORT FROM ADITS LOOK LIKE FOR ME? 

Specialist support from ADITS starts with CyberShield, a cyber security service designed around SMB1001. 

CyberShield puts 24/7 threat monitoring alongside the written policies and plans your insurer asks to see, and your team gets cyber awareness training. If you’d rather have IT and security under one roof, it sits within ADITS’ managed IT services.  

You keep the say on every priority and every dollar. 

SUMMARY 

Outsourcing cyber security doesn’t touch the IT provider who switched on your multi-factor authentication. It picks up the one job their agreement never mentioned, and leaves you with a gap analysis that says what to fix first and whose desk each fix lands on. 

At your next renewal, you type a date into that field, with a report and a plan behind it. You hit submit, and you relax. 

Explore specialist support for your business with ADITS’ cyber security services. 

FREQUENTLY ASKED QUESTIONS 

HOW MUCH WOULD SPECIALIST CYBER SECURITY SERVICES COST ME? 

The cost of specialist cyber security services depends on the size of your environment and whether you need a one-off engagement or ongoing support. 
 
A single assessment for a 20-person office is a smaller job than continuous monitoring across three sites. Ask each provider to scope your systems before quoting, and check whether fixing what the assessment finds is included or priced after the report. For ongoing support, ask whether the monthly fee is per user, per device or flat. 

HOW OFTEN SHOULD I REVIEW MY CYBER SECURITY MATURITY? 

Review your cyber security maturity at least once a year, and again after a significant change.  
 
Line the review up with your insurance renewal, and the date in that field stays under a year old. A new site, a new core system or a Copilot rollout all count as significant changes. Between reviews, your roadmap gives your IT provider a list to work through, so each review picks up where the last one finished. 

IS MY BUSINESS TOO SMALL FOR SPECIALIST CYBER SECURITY SERVICES? 

Your business isn’t too small for specialist cyber security services, because the support scales to you and SMB1001 is written for small and medium businesses. 
 
SMB1001’s tiered levels let a five-person practice start with the controls that matter most and build from there. A practice that size still holds client records and still gets the insurance questionnaire. It just has fewer people to work out the answers. 

What Is A Cyber Security Breach?

In 2024, over 80% of reported data breaches involved human error or stolen credentials. That means most cyber incidents aren’t the result of elite hackers cracking advanced firewalls. Instead, they’re caused by everyday slip-ups, weak passwords or overlooked software updates.

So, what is a cyber security breach exactly? And how can it affect your business? In this guide, we’ll explain how breaches happen, what they can lead to, and the key steps you can take to protect your systems, data and people.

What is a cyber security breach?

A cyber security breach happens when someone who shouldn’t be able to access your systems, networks or data manages to do so. It’s a type of security incident—like a digital break-in—where the attacker doesn’t force open a door, but instead sneaks in through a weak password, a phishing email or an unpatched vulnerability.

These breaches can lead to stolen personal data, identity theft, halted operations or even malicious software like ransomware. And it’s not just big companies at risk. Cyber criminals often target small and medium-sized businesses because their defences are easier to bypass.

How do cyber security breaches happen?

Most breaches don’t happen through high-tech hacking. They happen because of simple, avoidable gaps in security. Here are some of the most common ways breaches occur:

  • Human error: Clicking on suspicious links, opening phishing emails, or accidentally exposing data. This often happens when employees are rushed or unaware of common scam tactics used by attackers.
  • Weak or reused passwords: Easy-to-guess credentials are one of the most common entry points. Cyber criminals use tools to crack simple passwords in seconds or test stolen credentials across multiple platforms.
  • Outdated software: Failing to install updates or patches leaves known vulnerabilities open. If a business hasn’t updated its systems, hackers can take advantage of these unpatched vulnerabilities to gain access to sensitive data like intellectual property.
  • Lack of monitoring: Without 24/7 monitoring, threats can go undetected for weeks. This gives attackers more time to steal data, move across your network, or install malware.
  • Unsecured devices: Lost or stolen laptops and phones without proper protection. If these devices don’t have encryption or remote wipe capabilities, anyone who finds them could access personal information or sensitive business documents.
  • Insider threats: Disgruntled employees or careless internal users with access to sensitive systems or financial information. Not all threats come from outside. Someone within the business might misuse access or leak data intentionally or by mistake.
  • Social engineering: Manipulating people into giving up access or information—for instance, tricking someone into sharing passwords or clicking malicious links. These attacks often appear legitimate, which is why cyber security awareness training is so important.

What can a breach lead to?

A cyber breach can have serious long-term consequences for your business. Even small breaches can cause major damage, including:

  • Data theft or exposure: This includes sensitive information, financial details, like credit card numbers, or your business IP.  Once stolen, this data can be sold on the dark web or used to target your clients and partners.
  • Downtime and lost productivity: Systems can be locked or taken offline entirely. This can bring operations to a standstill and stop your team from doing their jobs.
  • Financial loss: From ransomware payments, fines, legal fees or recovery costs. Even a minor incident can result in thousands of dollars in direct and indirect losses, especially if malware attacks spread across systems.
  • Reputational damage: Losing customer trust can be hard to recover from. Clients may hesitate to work with a business they perceive as careless with their data.
  • Regulatory consequences: Especially for businesses in health, finance, or legal industries. Data breaches can lead to investigations, penalties, and the need to report incidents to authorities or clients.
  • Stress and internal disruption: This is where your team ends up putting out metaphorical fires instead of doing their job. It drains resources, delays projects and can take weeks (or months) to fully resolve.

How to prevent a cyber security breach

Cyber threats can hit fast and unexpectedly. With the right practices in place, however, you can dramatically reduce the risk of a security incident. Here are seven key steps every business should take to stay protected:

1. Use multi-layered security

Combine tools like firewalls, antivirus software, endpoint protection and email filtering to cover all entry points. Each layer defends against different types of threats. This makes it much harder for attackers to slip through the cracks.

2. Keep your systems updated

Outdated software is one of the most common ways cyber criminals get in. Regularly installing patches and updates helps close known vulnerabilities and keeps your systems resilient against the latest threats.

3. Enable multi-factor authentication (MFA)

MFA adds a second layer of protection to your login process, like a one-time code or authentication app. Even if a password is compromised, MFA can stop intruders from getting any further.

4. Train your team

Your people are often the first target in a cyber attack. Regular training helps staff identify phishing emails, suspicious links and risky behaviour. This turns them into your first line of defence rather than a weak spot.

5. Set strong password policies

Encourage the use of long, complex passwords and avoid password reuse across accounts. A password manager can help your team keep things secure without relying on memory.

6. Monitor 24/7

Cyber attacks don’t keep business hours. With continuous monitoring, threats can be detected and acted on before they cause serious damage, giving you peace of mind around the clock.

7. Back up your data

Regular, secure backups are your safety net. If a breach, social engineering attack or hardware failure occurs, a strong recovery plan means you can restore systems quickly and avoid costly downtime or data loss.

Protect your business from cyber threats today

Cyber threats are constantly evolving, but so are we. With ADITS’ proactive monitoring, tailored IT solutions, and expert training, you can stay one step ahead of cyber criminals.

Reach out today for a consultation and let ADITS help you secure your systems, protect your intellectual property and safeguard your personal data.

6 Cyber Security Mistakes SMBs Make (and How to Avoid Them)

Think your business is too small to be targeted by a cyber attack? Think again. 

Far from being too small to matter, SMBs are often prime targets for cyber criminals – as they can be seen has having few defences in place, being less resourced, less prepared and rarely equipped with dedicated IT or security teams. 

The reality is, many SMBs want to do the right thing when it comes to cyber security, but feel overwhelmed by the number of options available, costs involved and best actions to take.  

While these challenges are understandable, doing nothing isn’t a safe option. Don’t let cyber security get put in the “too hard” basket or become a one-off project you tick off and forget. It’s an ongoing journey that should evolve as your business grows. 

Want to dive deeper into cyber security or get a refresher on the basics? Check out our in-depth guide: What is cyber security and how can you be protected? 

Let’s unpack some of the most common cyber security mistakes SMBs make, so you can start building awareness as a first step towards better protection.  

Mistake 1: Neglecting Basic Cyber Hygiene 

A strong cyber security posture doesn’t always start with fancy tools. It can start with the basics. Consider the following.  

1. Weak Passwords 

Simple, reused, shared (or even, non-existent!) passwords are some of the most common vulnerabilities cyber attackers exploit. A reliable password management tool and multi-factor authentication (MFA) can close the gap. 

 2. Skipping Software Updates

Delaying critical updates leaves known vulnerabilities open. While not every update needs to be urgent, ignoring them shouldn’t be the default. Prioritise updates that fix high-risk issues, and set a patching schedule for everything else. 

 3. Firewalls Lacking the Right Fit 

Some businesses invest in complex tools without a clear understanding of what they need them to do. Others don’t have a firewall or intrusion detection system in place at all.  

There are a number of factors that apply when choosing the right firewall for a business network, such as network size, management expertise, scalability, threat protection needs and cost. 

Start by assessing your overall security posture, then choose a solution that fits your size, risks and capabilities, to complement your needs – ensuring it is configured correctly from the outset and continuously monitored for any changes or further configurations.  

Mistake 2: Underestimating Insider Threats 

Insider threats are often overlooked, but they can be just as damaging as those that are external. The OAIC reported receiving 27 notifications between July-December 2024, affecting 416 individuals.  

Employees, contractors or partners with access to sensitive information can unintentionally (or intentionally) compromise security. It could be mishandling data, falling for phishing scams, or in some instances, deliberate misconduct. 170 notifications of unintentional human error were made to the OAIC between July-December 2024, representing 683 individuals affected.  

These risks need to be addressed. Protect your business by limiting access based on role, implementing monitoring systems and other safeguards from within, like educating your team. 

Mistake 3: Lack of Employee Training 

Even the best cyber solutions can’t protect your business if your team isn’t equipped to use them, or spot the warning signs of an attack.  

Phishing scams, suspicious links and social engineering tactics are designed to exploit human error, not technology. Without regular cyber training, staff can unknowingly become the weakest link in your defence.  

Offer cyber awareness training that’s ongoing, accessible and tailored to your business (which can make it more relevant and engaging for each individual). Empowering your people with knowledge is one of the most cost-effective, practical and impactful ways to strengthen your cyber security posture.

Mistake 4: Ignoring Security for Mobile Devices  

Mobiles can be overlooked in cyber security planning. The thing is, they carry the same risks as desktops, especially when used for work.  

As your team members work on the go, check emails and access cloud-based apps, unsecured mobile devices can expose your business to serious threats.  

At a minimum, SMBs should use mobile device management (MDM) software to enable remote wiping, enforce encryption and restrict access to sensitive data.  

If employees are using corporate mobiles, clear controls are a must. It’s a part of protecting your broader network. 

Mistake 5: Not Having a Data Backup and Recovery Plan 

What would happen to your business if you lost access to data – either due to ransomware, hardware failure or human error? In many cases, SMBs don’t have a reliable way to bounce back.  

If an accident or worst-case scenario should occur, having a solid backup and recovery plan can support your business to minimise downtime and get your operations back on track.  

You may be leveraging in-built backup features from your current platform (like Microsoft 365), but these are typically basic data protection features only. Since they operate within the same platform as the primary service, they lack vendor or carrier redundancy—meaning if the platform itself experiences a failure or compromise, both your primary data and backups could be affected. This setup may not be sufficient to support comprehensive recovery in the event of a serious incident.. Consider gaining support from a specialist with cyber services to:  

  • retain copies of all your data 
  • use different backup media – to safeguard against physical damage 
  • keep offsite copies – such as cloud back up to protect against localised disasters.  

When things go wrong, knowing how to restore critical systems quickly and having a recovery plan is your safety net.  

Mistake 6: Disregarding Cloud Security 

Just because your data is in the cloud, doesn’t mean it’s automatically safe. Many SMBs assume their cloud provider handles all aspects of security. But in reality, it’s a shared responsibility. You cannot outsource your risk—your business remains accountable for protecting personal and sensitive data. The OAIC makes this clear: even when using third-party cloud services, the responsibility for data security and compliance rests with you. 

While providers secure infrastructure, SMBs are still responsible for user access, configurations and protecting the data itself.  

Misconfigured settings, weak passwords and ignoring access controls can open the door to breaches.  

Secure your cloud environment by knowing what you’re responsible for, enabling MFA, and regularly reviewing permissions. Before selecting any cloud or application provider, conduct a thorough Vendor Risk Assessment or third-party risk assessment to evaluate their security posture and compliance. Remember, the convenience of the cloud should never come at the cost of security. 

Treating cyber security as an afterthought can leave your SMB exposed to unnecessary and preventable risk. Don’t let it fall off your action list or let it be a set-and-forget task. With the right steps and support, even small improvements can have a big impact. 

You don’t have to tackle cyber security alone. Learn how ADITS cyber security services are designed to protect and support SMBs, every step of the way. 

Why Executive Leaders Are Critical to Cyber Security Strategy

Your organisation’s cyber security shouldn’t be rest solely on the shoulders of your IT department. In today’s complex digital landscape and in the face of increasingly advanced cyber threats – it’s whole-of-business imperative. And it’s up to executives to lead the charge.  

Your leadership team is essential for driving your cyber security strategy forward. Why? Without knowledge, buy-in and promotion from leaders, your business’s efforts can lack direction and urgency. Executives are essential for guiding the way, maintaining resilience against evolving threats and making security a priority throughout every level in your organisation.  

Proactive involvement, from the top down, creates a solid foundation for your cyber security initiatives to be effective.

Essential Cyber Security Responsibilities for Executive Leaders 

As an executive leader, you have an essential, active role to play in driving your organisation’s digital security, setting the tone and supporting team members to be proactive and prepared. Here are the key areas where your involvement can have a big impact.   

1. Lead Efforts to Identify Vulnerabilities

Champion regular security audits and assessments to identify vulnerabilities before they can be exploited. Don’t wait for an attack to realise what areas need attention. The earlier you identify potential threats, the less damage they can cause. 

2. Prioritise Threat Mitigation and Incident Response

When a cyber incident occurs, time is of the essence. You and your team’s ability to act quickly and proactively can minimise potential damage, downtime and data loss. Here’s where clear, actionable plans/processes can make a difference (more on this to follow) – as well as ensuring your team feels confident and familiar with these to address threats quickly and effectively.  

3. Support Training, Awareness and Education Efforts 

Training is a must for an effective cyber security strategy, particularly for executives, but don’t do it just to tick a box. Be a champion for continuous training initiatives. Understand the benefits of cyber security awareness training and consider cyber security training certificates. Encourage your people to keep their knowledge and awareness up to date, recognise threats and follow best practices. Your commitment to education is a great way to support well-informed, proactive teams. 

4. Foster a Security Culture

Embedding cyber security into your organisation’s DNA starts with leading by example. Ensure your team understands the importance of a security-first mindset, create opportunities for ongoing conversation and encourage them to raise concerns or suspicious activities. Embedding a security culture may take time and consistency but, overall, makes security initiatives significantly more effective.  

Owning these priorities sets the stage. Next, let’s explore the decisions and actions you can take to put that ownership into practice. 

Strategic Actions You Can Take Now 

As a decision-maker, you’re in the driver’s seat for your organisation’s cyber security success. Consider the following key actions to make security a part of your leadership legacy.  

1. Invest in Cyber Security Resources

Can you connect your teams with the right resources or partner with a trusted external expert to fill in the gaps? Committing to cyber security resources demonstrates your understanding of this essential topic and supports your team to develop the knowledge and skills they need to keep your business safe.  

2. Implement Clear Policies 

Offering training and resources is a great first step. Think of governance framework, policies and procedures as a way to build on this foundation. It’s on you and your leadership team to administer clear, actionable policies for your organisation (and ensure they’re actively followed!).  

Your policies may cover important areas such as:  

  • access controls – who has access to sensitive data 
  • incident response – how team members should respond to incidents 
  • acceptable use – how technology (emails, internet access, social media, CRMs) should be used 
  • data security – data encryption, storage, procedures for handling sensitive data 
  • password management – requirements for strong passwords, and MFA
  • more.  

Keep in mind that these policies aren’t set and forget. They should be embedded within day-to-day conversations and operations. 

3. Stay Informed 

You don’t need to be a cyber security whiz, but you do need to know enough to make decisions that protect your business and support your people. Stay up to date with current trends, risks and solutions. Spending time completing cyber security training for executives or completing a cyber security training certificate can go a long way in developing your confidence, and ensuring you feel prepared to lead your team through potential challenges. 

Consider these actions as building blocks for shaping a strong, long-lasting cyber security strategy – safeguarding your organisation’s most important assets for the long run. 

Ready to take your cyber security leadership to the next level? Find out more about tailored cyber security training for executives or get in touch to find out more about cyber security protection for your business.

What Is A Cyber Risk Assessment And Does Your Business Need One?

Did you know that small businesses are the target of 43% of cyber attacks, and shockingly, 60% of them are forced to shut their doors within six months of an attack. 

This is a sobering reality check that highlights the critical importance of businesses taking proactive steps to defend against cyber risks – now more than ever. 

While this sounds alarming, a clear solution exists: cyber risk assessment. Let’s explore everything you need to know about this systematic approach and how ADITS can help keep your business secure.

What is a cyber risk assessment?

A cyber risk assessment is a systematic process that helps uncover potential threats and vulnerabilities lurking within your information systems. Think of it as a wellness check for your business’s digital environment, pinpointing weaknesses in your defences before a cyber attack has the opportunity to break through.

For example, a cyber risk assessment might reveal that your organisation’s outdated firewall isn’t equipped to block newer forms of malware, or that employees are unknowingly using weak passwords, making it easier for hackers to breach your network.

By assessing risks head-on, businesses can make smarter decisions about where to strengthen their defences, keeping their digital assets secure and resilient in the face of ever-evolving threats. 

The Cyber security and Infrastructure Security Agency (CISA) highlights that these assessments play a major role in helping businesses truly understand how cyber threats can impact their operations at every level. This includes understanding how threats could disrupt your core mission, affect critical functions, and even tarnish your public image. 

With this clear picture, businesses can shape their cyber security strategies to support their bigger goals, ensuring digital security becomes a strong ally rather than an obstacle.

What are the main components of a cyber risk assessment?

A comprehensive cyber risk assessment involves six key steps, each aimed at uncovering and tackling any potential threats to your business’s digital landscape. Let’s take a detailed look at these important components:

1. Asset identification

The first step in a cyber risk assessment involves cataloguing everything within your digital environment, from hardware and software to data and network components. This helps pinpoint your most valuable assets and focus your security efforts where they’re needed most. To make this clearer, here are some examples of asset identification:

  • Identifying customer databases containing sensitive personal information: This involves determining where the data is stored, whether it’s on internal servers, cloud storage, or third-party platforms, and mapping out who has access to it.
  • Listing essential hardware such as servers and employee devices: This includes taking stock of all the devices that connect to your network, from desktops and laptops to smartphones and even smart devices. It’s important to know their configurations and how they’re being used to spot any potential security gaps.
  • Documenting software tools like CRM systems and cloud storage platforms: This is about keeping track of all the software you rely on, whether it’s a CRM, file-sharing system or accounting tool.

2. Threat analysis

This next step is all about identifying the potential threats that could take advantage of weaknesses in your systems. These threats can come from many places, both inside and outside your business. 

Outside risks include hackers, ransomware, or phishing attacks, while inside threats could stem from accidental errors or employees not being aware of security best practices. Here are a few examples to give you a clearer picture of these threats in action: 

  • A phishing email could trick employees into sharing login credentials: A phishing attack typically involves an email designed to look like it’s from a trusted source, like a colleague or a well-established company. The email might ask the recipient to click on a link or download an attachment, unknowingly giving attackers access to sensitive information.
  • Malware could enter your system through unsecured third-party apps: Many businesses rely on tools like project management software or communication platforms. However, If these aren’t properly vetted, or have security flaws, they can open the door to malware. 
  • Insider threats, like an employee misusing their access, can lead to data breaches:  Often, the biggest risks come from within the company. This can happen if an employee intentionally misuses their access, like a disgruntled worker leaking confidential information, or accidentally, such as by falling for a phishing scam.

    The threat analysis step helps strengthen access controls and ensures that employees are fully aware of their responsibilities when it comes to handling sensitive information.

3. Vulnerability assessment

After identifying potential threats, the third step is to take a closer look at where your systems might be vulnerable. This can mean spotting things like outdated software, weak passwords, or security flaws in applications that haven’t been patched yet. 

These gaps are the perfect entry points for cybercriminals, so it’s important to go through your systems carefully and identify any areas where defences may be slipping. Here are three common vulnerabilities:

  • Unsecured network connections: If your Wi-Fi network or internal systems are not properly secured, they can be easily accessed by unauthorised users. For instance, a guest Wi-Fi network without encryption or weak security settings could allow attackers to gain access to your company’s internal network and sensitive data.
  • Unpatched software vulnerabilities: Applications and operating systems regularly release security updates to patch vulnerabilities, but if you ignore or delay these updates, your systems can become exposed.

For example, an outdated version of a popular application might have a vulnerability that attackers can exploit to gain access. Spotting a vulnerability like this gives you the opportunity to patch your software and systems, effectively closing the door to cyber criminals before they can take advantage.

  • Exposed ports and services: Sometimes, businesses leave certain network ports or services open without realising they’re accessible from the outside. For instance, an unused port might still be open and connected to a service that could be exploited.

4. Risk evaluation

As you’ve likely noticed from the vulnerabilities we’ve discussed so far, not all of them carry the same level of threat to your business. This is where step four – risk evaluation – comes into play. This step is about understanding which threats are most likely to happen, and what kind of impact they would have on your business.

Some risks may feel like a real immediate threat, while others might be lower on the scale, but still require attention. By evaluating both the likelihood and severity of different scenarios, you can prioritise your resources and focus on what really matters. Let’s explore some examples:

  • A ransomware attack targeting your financial records: This could be highly likely, especially if your business handles a lot of sensitive data, or if your security systems are outdated. The impact of such an attack could be devastating; therefore, this type of threat would call for immediate action, such as enhancing your backup strategy, implementing stronger firewalls, and ensuring employees are trained to spot phishing attempts.
  • A minor data leak involving non-sensitive information: While not as catastrophic, a small data leak – say, the accidental sharing of non-sensitive internal memos – can still have significant consequences. For example, clients might begin to question your ability to safeguard any kind of information, even if it’s not sensitive, which could harm your reputation. 

5. Control implementation

Once you’ve prioritised the risks, it’s time to put the right measures in place to protect your systems. The Control Implementation stage is where you take action to minimise or eliminate the risks you’ve identified.

These controls come in two main forms: technical solutions and procedural measures. Technical solutions often include things like firewalls, encryption or multi-factor authentication. Whereas procedural measures focus on how people within your organisation should act to stay secure. Here are several examples of how controls are implemented:

  • You might set up endpoint security software on all your devices to stop malware in its tracks and prevent unauthorised access before any damage is done. That way, whether it’s a desktop, laptop, or mobile phone, everything stays protected.
  • You might implement automated patch management, where a system automatically installs security patches and updates across all devices and software, keeping systems up to date and minimising vulnerabilities.
  • Another step might be limiting access to sensitive files based on what each employee does. For example, only the finance team would have access to payroll data, while the marketing team would only see client-related info.

6. Monitor and review

Cyber threats are always evolving, so your cyber security strategy can’t just be set once and forgotten. It’s an ongoing process that requires regular check-ins to make sure your defences are still holding strong. For example:

  • You might regularly check access logs to catch any suspicious activity that could point to a potential breach. This is a great way to keep track of who’s accessing what and make sure no one’s unexpectedly snooping around your sensitive data.
  • You could set up quarterly vulnerability scans to catch any new risks or weaknesses that might have been missed before. With tech always evolving, something that was secure before might not be anymore, so staying proactive is key.

Why cyber risk assessments matter for your business

As you can see, regular cyber risk assessments offer significant benefits that can’t be overlooked. Here’s why making them a priority is a smart move for your business:

  • Stay ahead with proactive risk management: By spotting vulnerabilities early, you can take proactive steps to shore up your defences before attackers have the opportunity to exploit them. It’s all about preventing potential issues before they even have a chance to become major problems.
  • Stay on top of compliance: Many industries have regulations in place that require businesses to conduct regular risk assessments. By staying on top of these assessments, you ensure you’re not just protecting your data but also meeting legal and regulatory requirements.
  • Minimise downtime: Cyber incidents can bring your operations to a halt, and that downtime can end up costing you. For example, imagine your email system going down after a cyberattack. Not only does it slow communication, but it can also delay customer orders and even lead to lost sales. Regular assessments help you catch issues like this before they get out of hand, saving you time and money in the long run.
  • Strengthens customer trust: Customers want to know their data is safe. By regularly conducting cyber risk assessments, you show you’re serious about protecting their sensitive information, which helps strengthen your relationships and earn their trust.
  • Gain strategic insights: Regular assessments uncover patterns and pinpoint vulnerabilities in your systems, giving you a clearer picture of where your cyber security efforts are working and where they need improvement. This knowledge helps you prioritise future investments in cyber security, ensuring you spend your resources wisely on measures that offer the most protection.

Real-world lessons for your business

Taking a close look at past incidents highlights just how important regular cyber risk assessments are in preventing future breaches. Here’s a real-world example that really drives this point home:

Target data breach: A wake-up call for cyber risk assessment

In late 2013, a massive cyber attack hit retail giant Target, compromising over 40 million credit card numbers and 70 million customer records. The attack started when hackers gained access to Target’s network through a third-party vendor. 

The attackers exploited security weaknesses in the vendor’s systems to steal login credentials, which they then used to breach Target’s network. Once inside, the hackers accessed a range of sensitive information, including customer credit card details and personal records.

This incident is a prime example of why cyber risk assessments are so important. A single vulnerable link in a vendor’s security setup became a doorway for cybercriminals, leading to $162 million in financial losses for Target, along with an outburst of lawsuits from customers, banks and shareholders.

The lesson here? Target’s breach is a stark reminder of how a single weak link can endanger an entire organisation. A thorough risk assessment would have helped Target identify this vulnerability before it was exploited, allowing them to strengthen security protocols with their vendors and ultimately prevent the breach. 

For smaller businesses, the stakes are just as high, and with fewer resources to recover, proactive risk assessments are even more essential.

How ADITS can strengthen your cyber security with comprehensive risk assessments

As you’re now well aware, cyber risk assessments are essential for spotting vulnerabilities and threats before they turn into expensive headaches. 

At ADITS, we specialise in providing customised risk assessments designed to shield your business from cyber attacks and keep your operations performing on track. Here’s how we can support your business:

  • Tailored cyber risk assessments: We work closely with your team to understand your unique business needs and industry requirements, customising a comprehensive cyber risk assessment plan. This personalised approach ensures that all critical assets, from sensitive data to systems, are thoroughly evaluated for potential threats.
  • In-depth vulnerability scanning: By utilising the latest vulnerability scanning tools, ADITS identifies weaknesses in your network, software, and hardware before attackers can exploit them. This helps you stay one step ahead and reinforces your security posture.
  • Proactive threat detection: ADITS employs advanced threat detection technologies to continuously monitor your systems for signs of cyber threats. With early detection, your team can respond quickly to prevent breaches or limit damage.
  • Vendor risk management: As highlighted in the case study above, third-party vendors often serve as vulnerable gateways for cybercriminals to exploit. At ADITS, we include vendor risk management in our assessments to help ensure that your vendor relationships don’t unintentionally expose your business to cyber threats.
  • Regular risk reviews and updates: As cyber threats evolve, so should your risk assessments. ADITS provides ongoing reviews and updates to your assessments, making sure that your cyber security strategy evolves with emerging risks.

Take control of your cyber security with ADITS

Cyber risk assessments are much more than just a precautionary measure – they’re a vital step in protecting your business against costly breaches and disruptions. 

When you partner with ADITS, you’re gaining more than a comprehensive report. You’re gaining the expertise of a results-driven team that has supported over 800 businesses and 14,000 users. With clear insights, actionable recommendations, and tailored strategies, ADITS is dedicated to strengthening your security and protecting what matters most.

Don’t leave your security to chance. Reach out to ADITS today and take the first step towards a stronger, more resilient future for your business.


DISCOVER OUR SERVICES


Strengthening Your Cyber Security with the Updated SMB1001 Standard

Many small to medium-sized businesses (SMBs) are continually adapting to stay ahead in business. One way of achieving this is to safeguard against growing cyber threats through an annually updated standard.

The SMB1001 cyber security standard was designed to help SMBs attain this goal. It aims to address their unique cyber security challenges in terms of cost, flexibility, and scalability.

In this article, we’ll explore the 2025 updates to the SMB1001 and how they impact SMBs.  

SMBs are High-Risk Cyber Targets

SMBs continue to face increasing cyber threats, including ransomware, email compromise, and phishing scams. They can lead to severe financial losses, data breaches, and reputational damage.

The Annual Cyber Threat Report 2023-2024 cited how the Australian Institute of Criminology (AIC) described SMBs as “high-risk targets for ransomware attacks.” It also noted how the self-reported cost of cyber-crime went down 8% for businesses overall but went up 8% for smaller organisations.  

The SMB1001 Updates and What They Mean to SMBs

The recent changes to SMB1001 are a significant milestone in the world of cyber security frameworks and standards. It reflects DSI‘s commitment to enhance user experience and system performance.

The updates are part of a broader strategy and sets the stage for future advancements and improvements. It focuses on optimising various aspects of the standard and providing a better user experience.

Here are the key SMB1001:2025 updates:

New Control for Remote Desktop Protocol

SMBs certifying to Levels 3, 4, and 5 are encouraged to ensure that Remote Desktop Protocol (RDP) is enabled only over virtual private network (VPN) connections. RDP allows users to remotely access their computers, but it can be a target for cyber-attacks if not properly secured. This can reduce the risk of unauthorised access and data breaches, adding an extra layer of security.

Expanded Certification Levels

SMB1001’s multi-tiered certification model has been refined and expanded to better meet SMBs’ needs. The updated framework now has five distinct levels: Bronze, Silver, Gold, Platinum, and Diamond.

Each level has specific requirements that help organisations slowly but surely boost their digital protection.

With this approach, a business can start with basic security measures and progressively enhance their cyber security posture, as they grow and their needs evolve. It provides a clear roadmap with more achievable and more manageable steps.

Alignment with Global Standards

The updates allow SMBs to align with multiple standards and frameworks worldwide, including the ACSC’s Essential Eight, UK Cyber Essentials, and the US DoD’s CMMC. This ensures that SMBs can meet international security requirements, enhancing their credibility and competitiveness on a global market.

Further Improvements to the SMB1001 Cyber Security Standard

The standard will be reviewed annually to ensure it remains relevant against new and emerging cyber threats. This allows SMB1001 to adapt to the evolving cyber situation, incorporate the latest security practices, and address new vulnerabilities. It means SMBs can rely on the framework for up-to-date guidance, helping them deal with potential threats.  

What These Changes Mean for Existing SMB1001 Users

In summary, the SMB1001 updates are designed to benefit SMBs. They can more easily achieve risk reduction, easier implementation, and enhanced compliance after they switch to the updated framework.

Transitioning to the updated SMB1001 framework is a straightforward process for organisations already using the standard. First, they must perform a gap analysis to identify areas needing improvement. Next, they should update their policies and controls to align with the new requirements, focusing on enhanced security measures.  

Implementing the SMB1001 Framework through CyberShield

SMB1001 has revolutionised how SMBs approach cyber security. To further support SMBs in implementing this standard, ADITS built a unique solution called CyberShield.

CyberShield is a comprehensive cyber security solution designed to align seamlessly with SMB1001. It focuses on data privacy and compliance, with a combination of people skills, internal processes, and technology.

Practical steps for integration include conducting a risk assessment, implementing essential security controls, and continuously monitoring and updating security measures.

By adopting the SMB1001 framework enhancements, SMBs can work toward strengthening their cyber security posture. The recent updates provide a clear roadmap for improving their security measures more easily. With CyberShield, SMB1001 empowers SMBs to stay ahead of cyber threats, enhance their digital advantage, and meet community expectations.

Learn more about how CyberShield can meet your requirements. CyberShield-Banner-2

What is cyber security awareness training?

Cyber threats are evolving. In the early days of computing, most cyber attacks required a deep understanding of hardware and software systems. 

However, as the internet and digital networks became more widely accessible, the landscape of cyber threats shifted, giving cybercriminals more networks through which to launch attacks.   

In the battle against cybercrime, your employees can be your strongest asset. 

This is where cyber security awareness training makes all the difference. Rather than just relying on IT teams to safeguard systems, training helps employees understand their role in protecting sensitive data and avoiding common security pitfalls.

In this guide, we’ll cover everything you need to know about cyber security awareness training. From what it is and why you need it, to the major advantages it offers your business, we’ll explore how training can benefit you and strengthen your security.

What Is Cyber Security Awareness Training, and how does it protect your business?

Businesses worldwide are facing the growing threat of cyber attacks. While modern technology serves a key role in defence, human error remains a weak point. Careless actions or lapses in judgement are in fact a leading cause of data breaches for businesses, and with 83% of companies reporting a significant data breach, it’s more critical than ever for employees to have a strong awareness of cyber threats. 

Cyber security awareness training is a structured educational program designed to teach employees how to recognise, respond to, and avoid cyber threats. It focuses on building knowledge and practical skills to handle risks such as phishing scams, malware, and social engineering attacks.

By equipping your workforce with the tools to identify and neutralise threats, awareness training helps protect your business on multiple fronts, from data protection to financial security. When employees know how to handle sensitive information and respond to cyber incidents, they become integral to your business’s cyber defence strategy.

Unmasking the cyber threats that could harm your business

A major part of cyber security training involves understanding the scope and severity of common cyber attacks. Because the potential risks they pose are so severe – financial loss, reputational damage, or even legal consequences – understanding what they are and how to spot them is all-important for businesses. Let’s take a look at five prevalent cyber threats businesses face:

1. Phishing attacks

Phishing is one of the most common and dangerous cyber threats targeting businesses. It typically involves fraudulent emails, texts, or websites designed to trick employees into revealing sensitive information. 

These threats are often well-disguised as harmless communication from trusted sources, yet to trick the recipient into taking a specific action, like clicking a malicious link or downloading an infected attachment. Cyber security awareness training is crucial for teaching employees how to recognise red flags like phishing. 

2. Ransomware

Ransomware is a type of malware that encrypts a business’s data, rendering it inaccessible until a ransom is paid. This type of attack is not only financially devastating, but can also cause significant downtime, operational disruptions, and loss of critical data.

As ransomware attacks often begin through phishing emails or malicious downloads, it’s important to educate employees on how to recognise such attacks. ADITS specialises in identifying vulnerabilities like ransomware and provides proactive defence measures to help businesses implement the right security protocols. 

3. Malware and spyware

Malware and spyware are malicious software programs designed to infiltrate systems and compromise business data. Malware can steal information, corrupt files, or even allow hackers to gain remote control over a company’s systems.

Spyware, a subtype of malware, secretly collects user data, such as passwords, credit card details, and browsing habits. Attackers often deliver spyware through malicious links or downloads, which wreak havoc on an organisation’s security systems. 

Cyber security awareness training helps employees avoid downloading unverified attachments or clicking on suspicious links, turning them into a strong line of defence against malware and spyware threats.

4. Insider threats

Discussions about cyber security often focus on external cyber criminals. However, did you know that insider threats can be just as damaging? 

When employees or trusted individuals within the organisation either intentionally or unintentionally compromise company security, this is referred to as insider threats. These threats can involve data theft, espionage, or accidental errors that lead to vulnerabilities.

Raising awareness among employees about the potential dangers posed by insider threats is essential. ADITS has years of successful experience monitoring systems and access controls to help businesses detect and prevent unauthorised access or data misuse by internal staff.

5. Social engineering scams

Social engineering scams exploit human psychology. They take advantage of human tendencies like trust, curiosity and fear. 

Cybercriminals do this by manipulating individuals into revealing confidential information or taking actions that endanger security, often by creating a sense of urgency or appealing to emotions.

These scams usually come in the form of phone calls, emails, or direct interactions, where attackers pose as someone trusted, like a colleague or IT administrator. The goal is to deceive employees into bypassing security measures or handing over sensitive data.

How does cyber security awareness training work?

Cyber threats like those above can be eliminated with the right training. Effective cyber security awareness training goes beyond theoretical knowledge. It engages employees in interactive, real-world scenarios that help them identify and respond to potential threats. Here’s what you can expect from a well-structured training program:

1. Interactive learning modules 

When done right, a well-structured training awareness program leans on dynamic, interactive learning methods to keep employees engaged. While traditional cyber security training relied on static documents and long, routine lectures, effective awareness programs favour interactive modules designed to hold attention and improve retention.

These modules often feature a mix of formats, such as videos, quizzes, simulations, and scenario-based exercises, helping to stimulate participant involvement through active learning. 

Interactive learning example

Imagine a scenario-based exercise simulating a phishing attack. Employees are tasked with identifying suspicious elements in an email. In this exercise, they could consider the sender’s address, spot subtle typos, or identify urgency tactics commonly used by cybercriminals.

After making their choice, they gain immediate feedback explaining why the email was or was not legitimate. Carrying out a hands-on exercise like this reinforces theoretical knowledge while building confidence in one’s ability to spot real-world threats.

2. Real-life scenario simulations

For many of us, we learn best by doing. Awareness training takes this a step further by immersing employees in real-life scenario simulations replicating actual cyber-attacks. These exercises often closely mirror common cyber threats, such as phishing emails, fraudulent phone calls, or fake website login. 

These experiences provide employees a safe space to practise identifying and responding to cyber security challenges. Simulating cyber threats in an organised training environment helps employees learn and sharpen a range of relevant skills as well, including:

  • Recognise telltale signs: Employees learn to analyse suspicious emails, identifying indicators like misspelled domains, unexpected requests for sensitive information, or links that redirect to untrusted websites.
  • React well under pressure: Simulations test and improve employees’ ability to stay calm and follow protocols when encountering a potential attack.
  • Learn through safe errors: Mistakes made in these controlled environments become valuable teaching moments. Employees gain insight into what went wrong and how to improve, all without risking actual data breaches.

Real-life simulation example

A real-life scenario in awareness training could involve challenging employees with a simulated

phishing cyber threat. They receive an urgent email, asking employees to reveal sensitive information.

Imagine employees are encouraged to examine the situation by identifying warning signs, such as the unusual urgency of the message, grammatical errors, and an unfamiliar web link. After careful consideration, they must decide whether to report the message, ignore it, or take further steps.

After the simulation, participants are debriefed with a detailed breakdown of the red flags they missed or identified, equipping them with the knowledge to handle similar threats in the future.

3. Customisation and scalability

Cyber security awareness training isn’t a one-size-fits-all solution. For example, the threats and vulnerabilities faced by a small start-up differ greatly from those of a large enterprise.

To be truly impactful, training must be customised to meet the specific needs of the organisation. It must consider factors like the organisation’s industry, department, and individual roles. 

For instance, a healthcare organisation might prioritise data privacy, while a finance company may put stronger emphasis on protecting financial transactions. Different industries face unique cyber threats, and well-structured cyber security awareness training reflects these nuances.

Scalable training

As businesses grow, their operations become more complex, increasing their exposure to cyber threats. A robust security awareness program should have the ability to address risks that are relevant to the changing needs of the organisation. Scalable training ensures that as the organisation grows, its cyber security awareness remains a top priority.

What is ADITS’ approach to cyber security awareness training?

Every business has its own cyber security landscape, and at ADITS, we believe your training should reflect that. Our approach to cyber security awareness training is both strategic and personalised, tailored to your needs. 

Through years of conducting certified cyber security training, we’ve learned that the goal is not just to educate. It’s about empowering teams with the skills to recognise and respond to potential threats, no matter where they come from. Here’s how we do it:

  • Risk-aligned design: We work closely with you to understand your company’s specific cyber threats, industry regulations, and workforce structure. This ensures that our training content addresses your most pressing security challenges, from phishing attacks to insider threats.
  • Industry-specific focus: Whether you’re in finance, healthcare, or manufacturing, ADITS designs training programs that reflect the specific risks and compliance requirements of your sector.
  • Continuous improvement: Cyber threats are constantly evolving, so our training programs are regularly updated to reflect the latest tactics used by cybercriminals. Plus, we provide follow-up training and ongoing support to make sure your team stays ahead of emerging threats.

Creating an Effective Cyber Security awareness program with ADITS

Building a robust cyber security awareness program isn’t a one-time event. It’s an ongoing process that evolves alongside your business and the cyber threat landscape. 

At ADITS, we guide businesses through each crucial step, making sure your team is both aware of cyber threats and equipped to neutralise them. Here’s how we help you implement a comprehensive program:

1. Assessment and planning

Our first step with any client is to identify where their business is most vulnerable. We conduct a thorough risk assessment to pinpoint potential security gaps, from outdated systems and weak passwords to common employee behaviours that put your data at risk.

We work closely with you to understand your unique business environment, industry regulations, and specific threats, creating a tailored plan that addresses these vulnerabilities head-on. Having this foundation in place allows for clear objectives for your cyber security awareness program – as well as a roadmap that aligns with your business goals.

2. Continuous education

Cyber security isn’t something that can be taught in a single training session and then forgotten. As cyber threats evolve and new tactics emerge, it’s crucial that your employees remain up to date.

At ADITS, our cyber security awareness training emphasises the importance of continuous education. We design our programs as ongoing learning experiences, offering regular updates and refresher courses. This keeps your team informed about the latest threats, the newest trends in cyber crime, and the best practices for mitigating risks.

3. Regular testing

The best way to make sure your employees can handle a cyber attack is to simulate one. ADITS helps businesses implement regular testing through simulated cyber attacks, such as mock phishing campaigns. 

These exercises give employees the perfect chance to test their knowledge in real-world scenarios. It also helps identify weak areas where employees might need further training.

4. Metrics for success

Measuring the effectiveness of your training program is key to making improvements over time. At ADITS, we track important metrics such as employee participation, threat detection rates, and response times during simulated attacks.

Data points like these help gauge the success of the training program. We can use this data to adjust and update your program – for instance, to address emerging threats or to improve areas where employees may still be struggling. By continually evaluating your program’s impact, we ensure it stays relevant and keeps your business safe.

What are the major benefits for your business?

Now that you understand cyber security awareness training, let’s explore its major benefits. When your team is trained to spot and fight cyber threats, your security strengthens. The results? Real protection for your business on multiple fronts:

1. Reduced risks of attacks

A key advantage of cyber security awareness training is that it dramatically reduces successful attacks. According to various studies, businesses that invest in such training see a substantial drop in phishing incidents and other cyber-attacks. In fact, organisations with trained employees are up to 60% less likely to fall victim to phishing scams.

2. Cost savings

The financial impact of a successful cyber attack can be crippling. From the direct costs of addressing a breach to the long-term effects on client trust, the price of a cyber-attack can run into the millions.

The average cost of a ransomware attack is over $4.91 million! By preventing attacks through comprehensive training, businesses can avoid these devastating costs.

3. Employee empowerment

Employees are often the first line of defence in the fight against cyber threats. The right training can give them the confidence to spot suspicious emails, avoid risky links, and fully grasp how their actions can impact the company’s security. Having this empowerment can boost employee morale and contribute to a more proactive approach to cyber security.

4. Enhanced reputation

In today’s digital landscape, a significant portion of business transactions take place online, with customers entrusting companies with sensitive information. This makes client trust invaluable. 

Businesses that prioritise cyber security and demonstrate a commitment to protecting sensitive data maintain a strong reputation.

Cyber security awareness training helps ensure that your team follows best practices. This can directly contribute to securing client data and ultimately protecting your brand.

Stay ahead of cyber threats with ADITS

Cyber threats are targeting businesses of all sizes. Don’t leave your business exposed. Investing in cyber security awareness training is more than a quick safety measure against online threats. It’s a strategic move to protect your business’s future.

ADITS goes beyond generic security solutions. We tailor our training programs to address the unique challenges and risks your business faces. With interactive modules, real-life simulations, and expert guidance, our cyber security awareness training will give your team the skills to identify and eliminate threats before they escalate into costly disasters. 

Take a look at our cyber security services and get a free quote today. Let’s work together and build a resilient, safety-first culture that positions your business to thrive.


DISCOVER OUR SERVICES


What is cyber security and how can you be protected?

There are as many as 10 cyber attacks reported every hour in Australia. A report by America’s Cyber Defense Agency indicates that cybercrime is expected to cost the global economy over $10.5 trillion annually by 2025​. These staggering figures serve as a wake-up call, underscoring the urgent need for effective cyber security strategies that can adapt to an ever-evolving landscape of threats.

Cyber criminals are getting smarter, and unprotected businesses are feeling the strain. Given the expanding and ever-evolving nature of cyber threats, it’s never been more important to understand cyber security in today’s interconnected world. 

What is cyber security, then, and how can you make sure your business is protected from its harmful effects? In this guide, we will explore everything you need to know about cyber security. From what it is and its major threats, to how ADITS has all the right solutions to keep your business safe.

What is cyber security?

Cyber security serves as a digital stronghold protecting your information, networks and devices from unauthorised access and potential attacks. It’s like a fortress that adapts to evolving threats, creating a safe space in the digital world, where sensitive data can remain secure and private. 

The core of cyber security revolves around protecting three key aspects – confidentiality, integrity and availability. Confidentiality ensures only those with proper authorisation can access sensitive information. Integrity keeps data accurate and unaltered. While availability makes sure information and systems are accessible whenever needed.

Cyber security includes a range of practices that make up these three aspects, and these include:

  • Strong passwords: This is one of the simplest yet most effective ways to secure data. By creating complex, unique passwords for each account, users make it harder for attackers to gain unauthorised access. 
  • Firewalls: Acting as a barrier between trusted networks and potentially dangerous outside connections, firewalls monitor and control incoming and outgoing traffic, blocking suspicious activities.
  • Encryption: This practice scrambles data, making it unreadable without the correct decryption key. From emails to stored data, encryption ensures that sensitive information remains private. 
  • Antivirus software: These programs scan for, detect, and remove malicious software that can infect and compromise systems.
  • Two-factor authentication (2FA): Adding a second layer of authentication — like a one-time code sent to your phone — adds an extra layer of security beyond just a password
  • Regular updates and patching: Outdated software is a common vulnerability, often exploited by cybercriminals. Regular updates and patching fix known issues, making it harder for attackers to exploit weaknesses.

What are the main types of cyber security threats?

Cyber security threats come in all shapes and sizes, each with its own unique risks. Knowing the different types of threats can help you build a strong defence, so let’s break down some major cyber security threats you may encounter:

Malware

Malicious software, more commonly known as ‘malware,’ encompasses a variety of harmful programs like viruses, worms, ransomware and spyware. Cyber criminals create these programs to infiltrate systems, damage files, steal sensitive data or disrupt operations. 

For example, ransomware encrypts files and demands payment for their release, while spyware quietly collects data on a user’s activities without their knowledge. Malware is often introduced through infected email attachments, downloads, or compromised websites.

Phishing

Phishing attacks use deceptive tactics to trick individuals into revealing personal information, such as passwords or financial details. 

These attacks typically come in the form of fraudulent emails, messages, or websites that mimic trusted brands or institutions, leading unsuspecting users to click links or fill out fake forms. 

Social engineering

Social engineering relies on psychological manipulation rather than technical methods to gain access to confidential information. Attackers might pose as trusted individuals or legitimate organisations, using persuasion tactics to convince people to reveal sensitive data or grant unauthorised access.

For example, an attacker posing as a bank representative might call someone and claim they have noticed suspicious activity on their account. To ‘verify’ the account, they ask the individual for personal details and convince them to share sensitive information.

Denial of service (DoS) attacks

These types of attacks aim to overwhelm a system, network or website with excessive traffic or requests, causing it to crash or become unresponsive. Unlike other attacks that steal or manipulate data, DoS attacks focus on disruption, making online services temporarily inaccessible to users.

Advanced persistent threats (APTs)

APTs are sophisticated, long-term attacks typically used for espionage or large-scale data theft. Unlike quick, high-impact attacks, APTs are systematic. 

These attacks seek to infiltrate a network and remain undetected for months or even years. APT attackers gather data gradually, which allows them to collect valuable information over time without raising suspicion.

Protect your business with cyber security strategies

The sheer variety of harmful cyber threats is alarming. However, there are a range of cyber security strategies out there you can incorporate to protect your business. 

At ADITS, we offer a comprehensive range of cyber security solutions tailored to protect businesses from the growing landscape of cyber threats. Our approach covers key areas to address vulnerabilities, strengthen security, and ensure a proactive stance against potential attacks. Here’s a close look at what we provide:

1. Risk assessment and vulnerability management

We start by conducting a thorough risk assessment of your digital environment. We pinpoint potential vulnerabilities that cyber criminals could exploit. This includes identifying outdated software, weak access controls, and other areas that may expose your business to risk.

Throughout this process, we gain key insights. These help us craft a detailed security plan tailored to your business. This customised strategy not only strengthens your defences; it also ensures that resources are directed toward areas that need the most protection, creating a robust foundation for ongoing cyber resilience.

2. Managed threat detection and defence

ADITS offers round-the-clock monitoring to detect potential threats as they emerge. This allows us to spot suspicious activity in real time and respond swiftly before the threat escalates. 

This rapid, real-time response capability significantly reduces the impact on business operations and helps clients maintain their security posture in an ever-evolving threat landscape.

To offer an example of how this might work, imagine a financial services firm detects a series of failed login attempts from an unusual location. ADITS’ security team quickly verifies that these attempts are unauthorised and acts to block the suspicious IP address.

Following the incident, ADITS’ experienced cyber security team conducted an investigation to uncover how the attacker gained access. After discovering what happened, they provide the company with actionable recommendations to reinforce their security protocols. 

3. Network and endpoint protection

At ADITS, we employ an extensive approach to cyber security by implementing advanced firewalls, antivirus software, and intrusion prevention systems (IPS). This is to protect both a business’s network infrastructure and individual endpoints from a wide array of cyber threats.

This multi-layered defence strategy is crucial because cyber threats can exploit various vulnerabilities across a network and its connected devices. By securing both the network and endpoints, we ensure that every layer of one of our client’s digital infrastructure is protected.

To further highlight how our network and endpoint protection works, consider this example: Imagine ADITS helps an organisation by deploying advanced firewalls, antivirus software, and intrusion prevention systems to protect its network and endpoints from malware and phishing attacks. 

When a phishing email attempts to deliver malicious software, the antivirus detects it, while the firewall blocks access to the harmful site. This multi-layered approach effectively safeguards the organisation’s sensitive data.

4. Security awareness training

Employees often represent the first line of defence against cyber attacks. At ADITS, we provide comprehensive training programs aimed at equipping staff with the knowledge to identify and respond to various security risks.

We are providing these training sessions to foster a culture of security awareness within organisations, empowering employees to recognise suspicious activities and take appropriate action.

Security training has had remarkable results for businesses. A case study by KnowBe4 indicated that after implementing Internet Security Awareness Training (ISAT), companies experienced a huge reduction in phishing susceptibility, with some organisations reporting decreases of up to 75% in employees’ likelihood to click on phishing emails.
5. Data backup and recovery

As part of our comprehensive cyber security solutions, we also provide data backup and recovery to protect critical business information from loss during cyber incidents. 

For instance, in the event of a ransomware attack that encrypts company data, ADITS’ solutions allow businesses to quickly restore their information from secure backups, minimising disruptions and ensuring business continuity.

6. Compliance and regulatory support

Compliance and regulatory support is crucial for businesses operating in industries with stringent requirements, such as finance and healthcare. 

ADITS provides tailored solutions to help organisations navigate these complex regulations. This support not only protects sensitive data but also helps companies avoid potential legal complications and financial penalties associated with non-compliance.

To make this clearer, consider a healthcare organisation that must comply with HIPAA regulations to safeguard patient data. ADITS steps in to assess the organisation’s current cyber security posture. This involves taking a close look at their current cyber security setup and figuring out where they might not be meeting HIPAA standards. 

Once they identify any gaps, ADITS rolls out customised solutions, like using advanced encryption to protect patient records and providing employee training on how to handle data properly. This way, the organisation not only secures sensitive information but also ensures they’re ticking all the right boxes for compliance.

Fortify your cyber security with an IT partner that genuinely cares

There were a staggering 2,365 cyberattacks in 2023. Cyber crime is surging. With so many new victims every year, why leave it to chance?

Don’t become another statistic. At ADITS, we have partnered with countless businesses, providing comprehensive security services tailored to their specific needs – and we’re here for you too!

Take a look at our detailed cyber security solutions, get a free consultation, and allow your business to thrive while we ensure your data remains secure.


DISCOVER OUR SERVICES